



EDR and XDR are modern approaches to infrastructure protection in the face of growing cyber threats. EDR secures endpoints, while XDR provides centralized control and response across the entire IT environment. The right choice depends on the maturity of security processes, business scale and risk level.
How Cyber Threats Have Changed and Why Businesses Need a Next-Generation Approach
In recent years, the nature of cyberattacks has changed dramatically. Hackers increasingly use multi-stage scenarios, operate stealthily and target not only vulnerable devices, but also user behavior. The time between compromise and its consequences is getting shorter, while the potential damage is growing.
At the same time, older security tools are no longer enough. Traditional antivirus tools often lack the visibility and behavioral context needed to detect complex attacks. VPN does not control what an employee does after logging in. And the perimeter that once could be clearly defined is now blurred by remote work, cloud services and personal devices inside the corporate environment.
This is the context in which next-generation solutions, EDR and XDR, emerged. Their task is not just to record the fact of a breach, but to detect behavioral anomalies, predict risks and respond proactively before damage occurs.
What EDR Is and How It Works
Endpoint Detection and Response is a technology that helps security teams avoid getting lost in a stream of events and focus on truly suspicious signals. Unlike traditional antivirus tools, EDR does not simply look for malicious files. It tracks device behavior, analyzes process activity and collects data for further incident investigation.
The main strength of EDR is its ability to work in real time. As soon as an anomaly appears, the system can automatically contain it: disconnect the device from the network, isolate a malicious process or send a suspicious file for analysis. In critical cases, this helps win decisive minutes.
A typical EDR system includes:
- Continuous monitoring of device behavior.
- Detection of deviations from normal activity and unusual behavior.
- Automated threat response.
- Collection and analysis of data for digital forensics.
These systems also scale well and are suitable for both corporate networks and hybrid work models. They are especially effective in environments with a high risk of compromise, such as development teams, administrators or finance departments.
How XDR Complements and Strengthens EDR
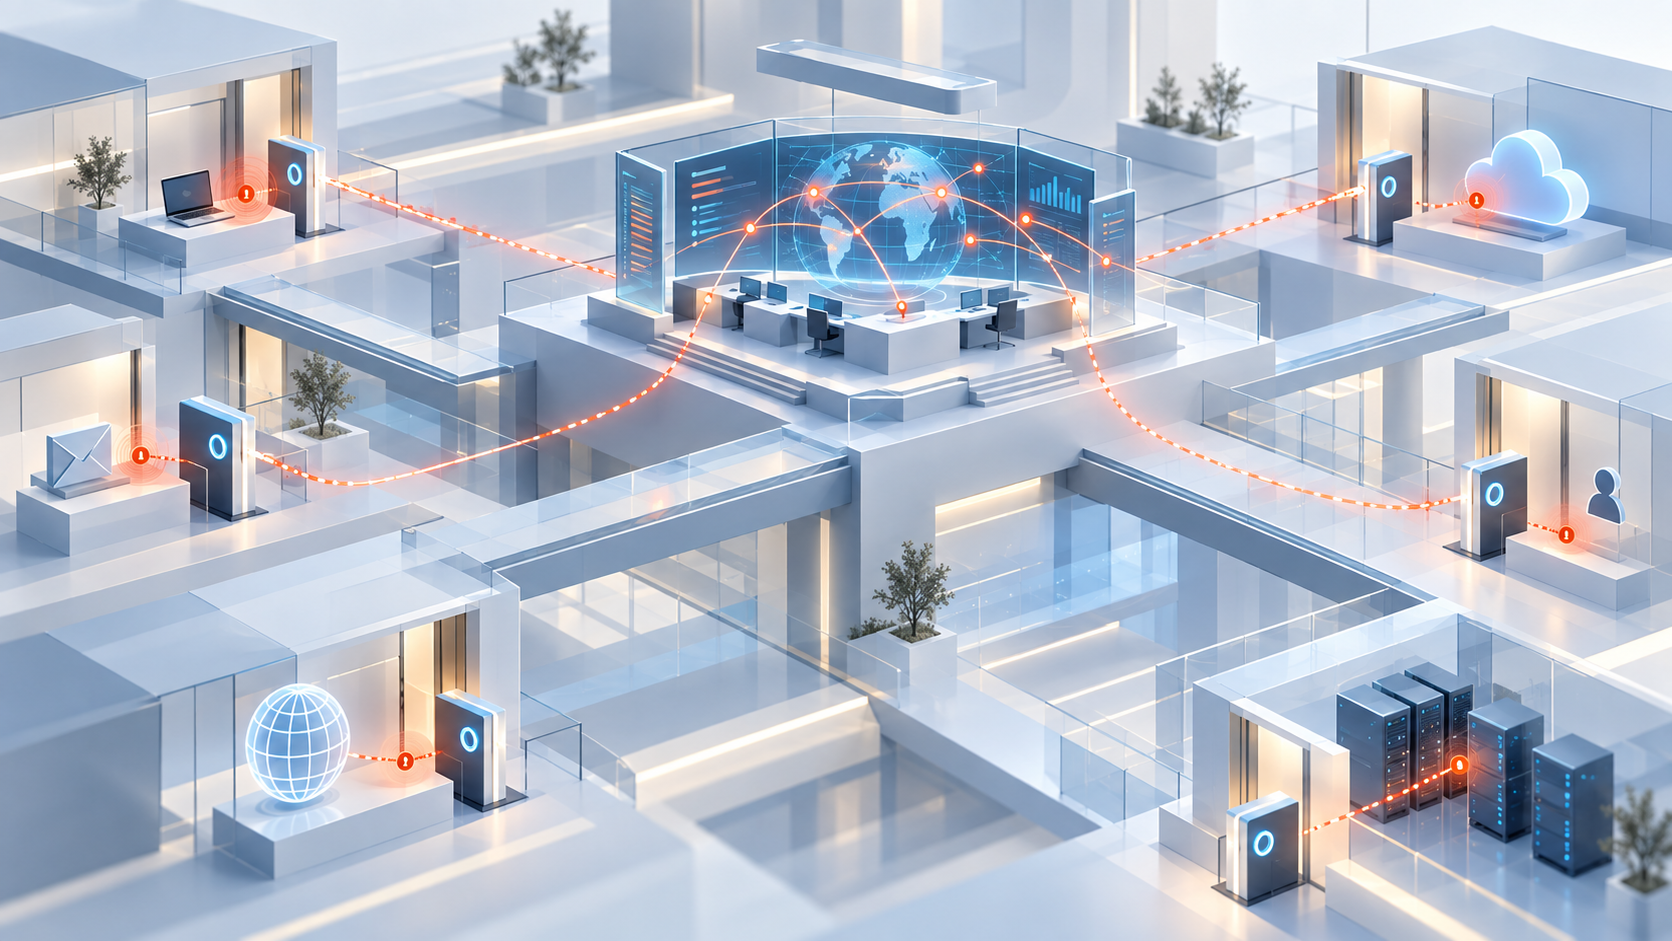
It is not just a data aggregator. XDR makes it possible to see connections between events. What looks like a minor deviation on one device may turn out to be part of a complex attack when compared with user behavior in the cloud or activity in a mailbox.
XDR enables teams to act based on the full picture, not guesswork. Instead of responding to incidents in isolation, you can understand where everything started, what has already been affected and how to limit the damage. A single console, centralized investigation and contextual analytics make XDR not just a tool, but a platform for building a mature security strategy.
What Is the Difference Between EDR and XDR: Comparing Coverage and Maturity
Although their goal is similar, protection against cyber threats, EDR and XDR differ significantly in coverage, automation capabilities and scale. One of the most common questions from security teams is: when is EDR enough, and when is it time to move to XDR?
| Criterion | EDR | XDR |
| Data sources | Endpoints only | Endpoints, email, network, clouds, identities |
| Context | Local | End-to-end across the entire infrastructure |
| Automation | Partial, within the device | Extended, with correlation across systems |
| Scalability | Limited to endpoint infrastructure | Centralized scalability, mature architecture |
| Resource requirements | Relatively low | Higher, requires preparation and process maturity |
A simple example: a phishing attack.
In EDR, the user’s device detects suspicious behavior, the antivirus isolates the file and automatic blocking may occur. However, the chain leading to the email service or cloud remains out of view.
In XDR, the system sees the email, identifies a mass mailing, flags unusual link clicks, blocks the login, isolates the account and launches an investigation with full context of the user’s actions.
Conclusion: EDR is an effective tactical tool for endpoint protection. But if an organization wants to see the full picture and respond to complex incidents, XDR becomes essential.
Where and How EDR and XDR Work: Practical Scenarios and Solution Architecture
EDR/XDR tools are used across industries, from manufacturing to education. Below are examples where they deliver the strongest impact:
Financial Sector
EDR helps protect workstations, terminals and ATMs from intrusions. XDR provides access control for payment systems, monitors anomalies in employee email accounts and connects events between cloud applications and network zones.
Manufacturing
EDR monitors engineers’ devices, while XDR helps prevent lateral movement, attackers moving from the IT network into OT, by tracking suspicious activity between production systems.
Healthcare
EDR blocks attempts to launch malware on doctors’ computers. XDR provides access control for electronic medical records (EMR), logs staff actions and helps prevent leakage of sensitive data.
Retail
EDR protects POS terminals and cash register nodes. XDR analyzes the entire chain: from suspicious emails to changes in ERP or CRM, encrypts data and detects mass attacks on retail network infrastructure.
Education and SMB
Small organizations can start with basic EDR protection and gradually expand coverage. XDR is especially useful when there is no internal SOC, as it aggregates events, reduces noise and improves response to threats.
What XDR Consists Of: Key System Components
XDR is not just a single product, but an entire security ecosystem where connectivity plays a key role. It brings together multiple data sources, processes them in a unified context and provides centralized response. For the technology to work effectively, its architecture must be complete and adaptive.
Typical XDR architecture:
Data sources
→ endpoints, email, cloud, network, user accounts
Event aggregator
→ correlation, filtering and normalization mechanisms
SIEM / SOAR, if available
→ deeper analysis, response automation
Incident management
→ built-in or external incident handling module
Key components of an XDR system:
- Endpoint protection, monitoring and protection of workstations, laptops and servers.
- Email security, control of incoming and outgoing email, anti-phishing and sandboxing.
- Cloud security, protection of cloud environments, including IaaS and SaaS, such as Microsoft 365, AWS and GCP.
- Identity protection, monitoring of user accounts, MFA, login control and access rights management.
- UEBA (User and Entity Behavior Analytics), behavior analytics for users and systems.
The central feature of XDR architecture is integration. All data must enter the aggregator in a unified format. This is achieved through log normalization, connectors and API integrations. Without this, XDR efficiency drops, the system cannot detect correlations between events across different zones.
How to Approach EDR/XDR Selection and Implementation: Practical Recommendations
Choosing between EDR and XDR depends on more than budget or brand. Much more important factors include the maturity of security processes, team structure and the company's technology stack.
Here are the key criteria to evaluate before making a decision:
1. Visibility Level: Is EDR Enough?
If critical threats can originate from more than just endpoints, and in most cases they do, broader visibility is required. XDR enables monitoring across email, cloud environments and networks, not just devices.
2. Presence or Absence of a SOC / Security Analytics Team
If you do not have an internal incident response team, XDR can serve as a “virtual SOC”, consolidating incidents, providing built-in automation and prioritizing events. At the same time, XDR also gives existing SOC teams additional capabilities and tooling.
3. Do You Already Have SIEM?
If a company already uses SIEM, XDR can either complement it with endpoint data or take over part of the response and automation workflows, especially if the SIEM solution lacks behavioral analytics capabilities.
4. Infrastructure Flexibility
Do you use a multi-cloud environment? Are there devices operating outside the perimeter, BYOD policies or offices in different countries? The more complex the technology stack, the more valuable XDR becomes as a connecting layer.
5. Resources and Budget
EDR is simpler and less expensive to deploy and can be implemented faster. XDR requires more architectural planning but delivers significantly greater value, especially in the medium and long term.
Where to Start: Infrastructure Implementation Stages
The first stage is auditing the current IT and security infrastructure. Which assets need protection? Where are the biggest risk areas? Which tools are already in use and which have become outdated?
The next step is defining priorities. Start with the most vulnerable areas: developer access to production environments, executive email accounts and external contractor connections.
Based on these findings, a PoC (Proof of Concept) is created, usually starting with EDR, allowing teams to test key detection and response scenarios.
After obtaining practical results, organizations can move toward XDR integration by connecting additional data sources such as email systems, cloud platforms, networks and identities, configuring automated policies and enabling event correlation.
The final stage involves training security teams and automating routine tasks. Without the involvement of SOC analysts and administrators, even the best technologies will not deliver meaningful results.
Common Mistakes and Myths
There are still many misconceptions surrounding XDR. Here are some of the most common:
"XDR replaces everything"
In reality, XDR is not a magic button. It is a coordination platform and does not eliminate the need for SIEM, EDR or manual analysis.
"EDR is enough"
Only if you have no email systems, no cloud infrastructure and no APIs. In practice, that scenario is increasingly rare, meaning EDR visibility alone is usually insufficient.
"XDR is expensive and difficult to implement"
There are phased implementation approaches adapted to different budgets. Organizations can start small and scale as threats grow.
"XDR = SIEM"
No. SIEM is primarily a log management platform. XDR is an active response platform focused on context, visibility and automation.
Conclusion: Strategy, Not Just Tools
EDR and XDR are not simply software products, they represent a new way of thinking about cybersecurity.
EDR addresses tactical challenges at the device level. XDR builds a broader strategy, covering the entire technology stack, from workstations and endpoints to cloud environments and email systems.
These technologies do not compete with each other, they complement one another. True maturity comes when a business creates an adaptive, scalable and automated incident response system.
The most important step is simply to begin. Even a small PoC can become the starting point for significant transformation.